


Pursue takedowns
We submit abuse reports to registrars, hosting providers and platforms, with evidence of phishing or brand impersonation, and follow up on the outcome.
EXTERNAL THREAT MONITORING & RESPONSE
Fake websites, Telegram scams, leaked credentials, keys on GitHub, dark web disclosures and ransomware posts — in one service.
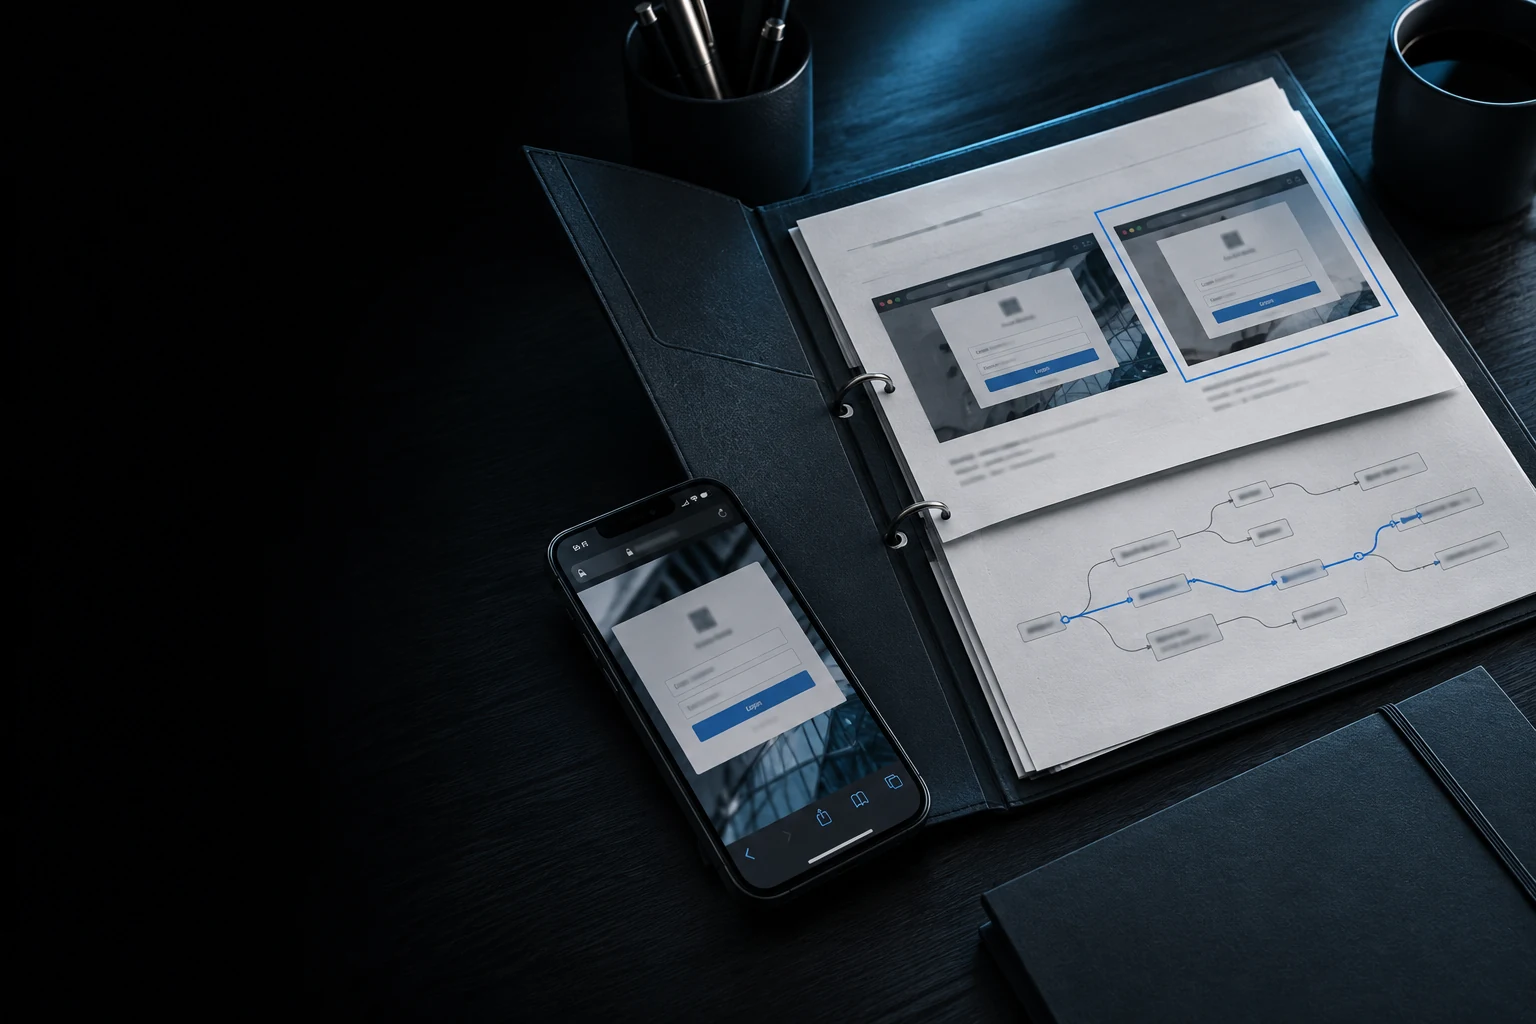
We monitor threats to your brand, employees and assets.

Sites impersonating your brand to steal credentials, seed phrases or cryptoassets.

Fake channels, bots and support accounts impersonating your company.

Addresses collecting stolen funds and scripts that drain cryptoassets.

Leaked employee credentials and signs of infostealer infections on their devices.

API keys, configurations and other secrets exposed in public GitHub and GitLab repositories.

Ransomware group posts about your company and claims that its data is being sold or exposed.
An analyst verifies the connection to your company and collects evidence. Our team then takes action.
We submit abuse reports to registrars, hosting providers and platforms, with evidence of phishing or brand impersonation, and follow up on the outcome.

We add confirmed scam addresses to the Match Systems AML database, monitor transfers and trace stolen funds.

We identify affected accounts, keys and repositories, and give your team priorities: reset credentials, revoke keys and check devices for infection.
We connect addresses and transfers, track stolen funds and prepare evidence for freeze requests.
Establish how the wallet is linked to the scam.

Record the confirmed address and its connection to the threat in our AML database.
Track onward transfers and connected addresses.
Prepare evidence and support requests to services and issuers that can freeze assets.
The relevant service or issuer decides whether to block or freeze assets.

The verified threat, supporting evidence and actions already underway.

Findings, linked addresses, submitted requests and the current status of work.
Threats identified, actions taken and confirmed outcomes for the month.
A clear status for every action
See what we found, who we contacted and the outcome of each request.
Your company and product names, official domains and accounts. For leak detection, include email domains, work services and repositories. Before launch, we agree on what to protect, team contacts and the response procedure.
An analyst checks the finding. We report phishing to platforms and providers, tag scam wallets in our AML database and track funds to support freezes. For leaks, we identify affected credentials and give your team specific actions.
Monitoring uses external sources. We do not need passwords or access to your internal network. Some sources may require domain verification.
We submit reports, gather evidence, trace funds and follow up on requests. The registrar, platform, service or issuer decides whether to disable a resource or freeze assets. We record their responses and next steps.
After an analyst reviews the finding, with further updates on response progress. Check frequency depends on the source; duplicates are grouped to avoid overwhelming your team.
We agree on what to monitor, how to respond and how to keep your team informed.
Message us on Telegram