


By August 2026, the use of artificial intelligence in attacks on crypto companies had ceased to be a theoretical threat. We see this directly in our investigative practice: the structure of incidents remains the same, but preparing an attack has become cheaper, communication with the victim more convincing, and the interval between first contact and asset withdrawal shorter.
The main point we want to establish is this: it is not that AI has learned to hack blockchains. It is the industrial-scale automation of attacks on trust, identity and transaction-approval processes. These are fundamentally different things, and confusing them prevents effective defenses from being built.
Why crypto services are a priority target
Crypto companies combine several characteristics that make AI-assisted attacks particularly profitable.
First is the scale of the potential loss. Compromising one account, one key or one signing procedure can lead to losses of hundreds of millions of dollars. The theft from Bybit in February 2025 alone amounted to approximately $1.5 billion, and the FBI officially attributed it to North Korean activity.
Second is the wide range of employees with access to critical infrastructure: developers, DevOps, security engineers, treasury, compliance, support and executives. Each is a separate entry point.
Third is dependence on external services: cloud platforms, GitHub, Slack, Telegram, Zoom, multisig providers and custody solutions. Attacks often come through a trusted integration rather than directly.
Fourth is distributed teams and remote hiring, where an employee's digital identity becomes the primary proof of who they are, and therefore the primary target.
Fifth is the speed at which stolen assets move. In our practice, the first significant movements occur within hours of a theft, while the window for an effective response narrows to tens of minutes—a timescale incompatible with manual escalation procedures.
How AI works inside the attack itself
AI rarely replaces traditional techniques. It fits into the existing attack chain and improves the efficiency of almost every stage.
During reconnaissance, language models take minutes to assemble and structure an employee profile: role, responsibilities, technology stack, likely access level, colleagues and communication style. The attacker receives not an abstract victim, but a description of a specific workflow they can insert themselves into.
At the intrusion stage, we increasingly see the ClickFix technique: the victim is led to copy and execute a terminal command themselves, under the pretext of 'fixing' a Zoom microphone, completing verification or installing an update. This bypasses a significant portion of defenses because the user performs the malicious action on a trusted device. AI generates a convincing technical context that makes an engineer or developer respond professionally rather than suspiciously.
A separate technical shift is malware that calls a language model during execution. Part of its logic is not hardcoded but requested dynamically: what data to collect, what commands to execute and how to modify its own code. The practical consequence for a crypto service is direct: signature-based detection loses effectiveness because the sample changes from one execution to the next. This creates the greatest risk on the workstations of developers, DevOps staff and wallet operators.
An important class of attacks bypasses MFA by stealing session tokens. The attacker often needs neither the password nor the second factor: intercepting an active session after the employee has authenticated is sufficient. Subsequent actions are performed through a legitimate, already verified account and appear routine to the system.
Synthetic identity: gaining entry through trust
In our assessment, the most dangerous direction is synthetic identity. Generative tools can create photographs, video, voice, documents and complete profiles sufficient to impersonate an executive, investor, customer, candidate or counterparty representative.
The key risk comes not from an individual element but from a combination of channels: moving from a messenger conversation to email, then to a video call, then to voice confirmation and an accompanying document. Each signal looks credible on its own; together they form an entirely artificial communication environment. In investigations of such incidents, we see that trust was established not by a technical exploit but by a real person's hijacked account and a plausible videoconferencing environment—even real-time generated video impersonating someone the victim knew.
The practical rule we recommend adopting is that video calls and voice are no longer independent proof of identity for financially significant operations.
 Forged identity
- Messenger and email
- Video call
- Voice confirmation
- Accompanying document
 Messenger and email
 Video call
 Voice confirmation
 Accompanying document
A synthetic employee instead of a compromised one
An extension of the same logic is a scenario in which AI is used not to deceive from outside, but to gain access inside an organization through recruitment. The operator is in a third country, uses the stolen identity of a citizen of another country and obtains a remote position with high-level access at a Western company. The résumé, cover story, technical interview and even a real-time deepfake during the interview are all generated and maintained with AI tools.
Once hired, this 'employee' is already inside the perimeter: they have legitimate credentials and access to repositories, infrastructure and sometimes wallet-related processes. The subsequent attack is carried out from within and looks to security systems like the normal work of a hired specialist.
The change in the threat model is fundamental. A company must account not only for the possibility of an employee being compromised, but also for the possibility of an attacker becoming an employee. For a crypto service, this means recruitment has ceased to be exclusively an HR process and has become part of the security perimeter.
Attacking the signing process
The central risk does not always involve stealing a private key. Often the goal is to get an authorized employee to sign a malicious operation themselves. AI is used here to impersonate colleagues, forge internal correspondence, justify an urgent transfer and create a false transaction context.
The Bybit incident demonstrated the severity of this threat class: infrastructure associated with a multisig operation was compromised, after which the attacker could alter the operation's logic and withdraw assets from a cold wallet. Technically, the signer saw one thing on screen but authorized another—the substitution occurred at the transaction-presentation layer, not at the key level.
The conclusion we consider most important is that multisig protects against compromise of one key, but does not automatically protect against compromise of the decision-making process. The signer must check not the description displayed by the interface, but an independently obtained representation of the transaction's actual parameters: recipient address, amount and contract being called.
Why familiar indicators no longer work
Several signals on which security teams have historically relied have lost their reliability. Poorly written email is no longer an indicator. A video connection is no longer proof of identity. Successfully passing MFA does not mean an employee is behind the device. Passing selfie verification does not mean the system is facing the document's real owner. Using a corporate account does not mean its lawful owner is acting.
Our investigative practice confirms this: in most major incidents over the past year, a technical vulnerability was not the key link. The key link was the exploitation of trust.
AI on the defense side
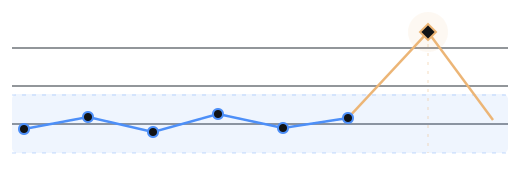
It would be wrong to present artificial intelligence solely as an attacker's tool. The same technology that scales attacks gives defenders a previously unavailable capability: establishing a behavioral baseline and spotting deviations from it in real time.
The practical model works as follows. Over several weeks or months, a machine-learning system observes the company's normal operations: when employees log in and from which devices, networks and locations; the usual sequence of actions; the speed of operations; typical API access; who initiates transfers and when; and how transactions are approved. An individual behavioral profile of the organization and each significant role within it gradually forms.
The system then works proactively. When an anomaly occurs—a login from a new device immediately after successful MFA, an unusual sequence of SaaS actions, access to wallet infrastructure at an unusual time, an abrupt change in withdrawal settings or signers, or an account-activity spike inconsistent with its usual profile—an alert is generated, and the critical operation can be suspended pending manual confirmation.
The value of this approach is precisely that it does not try to 'detect AI' at the entry point. It assumes that the attacker will eventually get inside with legitimate credentials and shifts detection to the behavior of an already authenticated session. Poor email language, deepfake quality and the persuasiveness of the cover story do not matter here; what matters is that the account's actions have diverged from its historical baseline.
This does not replace procedural measures; it reinforces them. Behavioral analytics addresses precisely the gap created by synthetic identities and stolen sessions: it sees not 'who claims to be who they say they are,' but 'what this account actually does and how closely that resembles its normal behavior.'
 Alert

Where defenders retain an advantage
AI also changes the post-compromise stage: stolen assets are split, converted, routed through cross-chain bridges and DEXs, sent to centralized services and then withdrawn into fiat or stablecoins. The attacker's objective is to break the visible link between the initial address and the final recipients, and automated route selection accelerates this process.
But defenders retain a fundamental advantage here. A synthetic identity may hide who was behind the attack, but it does not erase the history of asset movements already recorded on the blockchain. The transaction trail remains available for analysis regardless of how convincing the social engineering was at the point of entry.
At Match Systems, investigations combine several methods: clustering attacker addresses by behavioral patterns; tracing through bridges and DEXs to reconstruct the route even after a change of network; identifying interactions with centralized services where freezing is possible; and building a unified timeline linking on-chain asset movements with off-chain attack events. Without blockchain analytics, assets cannot be located; without cooperation with platforms, they cannot be stopped; without properly prepared materials, the case cannot be brought to law enforcement. The first hours are usually decisive: the earlier recipient addresses are recorded and requests sent to exchanges, the greater the chance of intercepting the assets before withdrawal.
Conclusion
The main mistake in assessing this threat is to treat AI as a new type of malware. In reality, it acts as a universal accelerator across the entire criminal chain: reducing the cost of reconnaissance, social engineering, identity creation, gaining access and scaling an operation.
For the crypto industry, this is particularly dangerous because the final stage of an attack is extremely short: one compromised identity, one approved transaction and potentially hundreds of millions of dollars.
The right question for a security team is therefore not 'was this email written by artificial intelligence?' It is whether an attacker using a synthetic identity, legitimate credentials and social engineering can gain enough trust to carry out a financially critical operation. If the answer is yes, whether AI is present in a particular attack is secondary.
The most realistic threat in the coming years is not an autonomous superintelligence hacking blockchains, but a highly automated criminal organization that creates convincing people, automates communication, infiltrates companies and takes over existing mechanisms of trust. Accordingly, defense must shift from 'protecting infrastructure against malware' to a model in which every critical identity, every privileged action and every financial operation is independently verified, regardless of how convincing the initiator appears.
Hot Stories
- News Bitget: reports of a possible $170M hack
- Investigations White-hat hackers exploit Liquid Network flaw to steal $320M BTC
- Investigations Symbiosis Recovers 15 BTC After Bitcoin Bridge Exploit
- Investigations Blockstream rejects ransom demand after $320M Liquid hack
- Investigations OFAC and DOJ Freeze $52M in Xinbi Crypto Laundering Network
- Investigations OFAC sanctions Shelbit and affiliates for $6.3B crypto flows
- Investigations Cronos halts blockchain after $75M Tectonic DeFi exploit
- Investigations EigenWallet and BTC–XMR Atomic Swaps: How Stolen Crypto Is Obscured
- Investigations More Markets loses $9.3M in Wrapped Flow exploit on Flow EVM
- Investigations Can Stolen Crypto Be Recovered? What Changes the Odds